
Free AI Approval Register Template
A Starter for Business Owners and Leaders
Most businesses don't have a clear picture of every AI tool running in their business. This template is the starting point.
An AI approval register is a simple record of every AI tool your business uses:
what it does;
what data it touches;
who approved it; and
who is accountable for it.
It doesn't need to be complicated. A well-structured spreadsheet is enough to get started.
We've built a plain-English starter template you can download and use today. No sign-up required.
What's included:
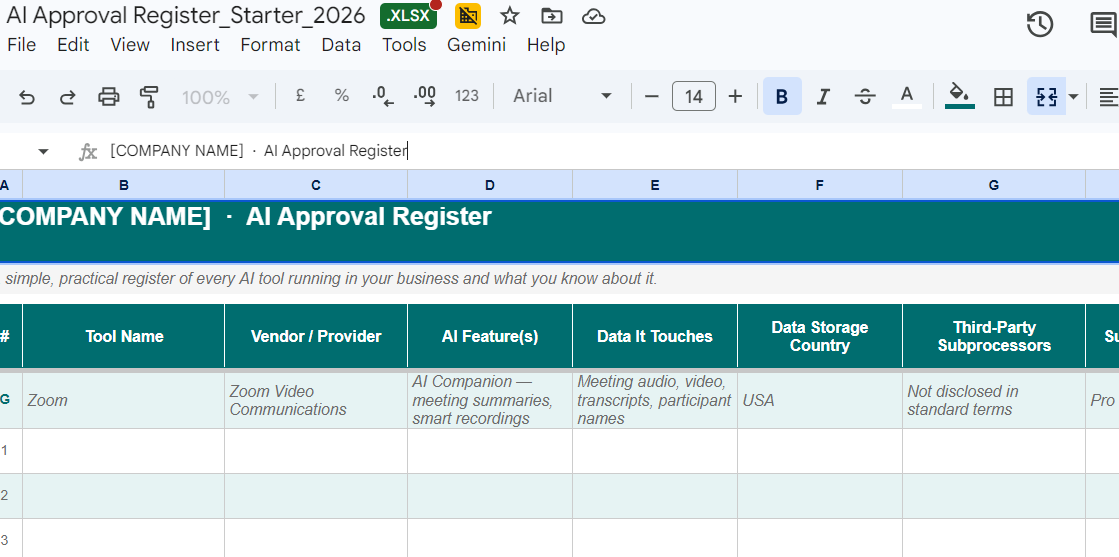
The register has two tabs. The first is your working register ready to fill in. The second is a plain-English guide explaining what each column means and why it matters.
The columns cover:
Tool name and what the AI features actually do
What data it touches such customer, employee, job candidates, financial, other
Where the data is stored and which country it's processed in
Whether third-party subprocessors are disclosed
Which subscription tier you're on (if applicable) because defaults vary significantly between tiers
Who approved the tool: a named person who made a deliberate decision
Who is accountable: a named individual, not "the IT team".
Whether the terms, contract and data processing agreement have been reviewed and align with your countries privacy requirements as well as your businesses best practices. If the tool doesn’t not meet then implement appropriate privacy controls, conduct a data impact assessment, or investigage into another vendor that is more aligned to your business obligations.
When the terms, contract and data processing agreements were last reviewed and when to review them next
Date of when a impact assessment was carried out (See Glossary available in the downloadable spreadsheet)
Status and notes
and more (‘How to Use this Register’ tab will provide guidance on how to complete the register)
NOTE: This AI Approval Register is designed for business owners and founders who don’t have a Data Protection Officer, Privacy or GRC background, so it’s deliberately simple by design.
Why you need this:
Most businesses don't know exactly what AI is running inside their software. Tools they've used for years have been quietly updated with AI features often switched on by default, often without a separate notification. And vendors update their terms silently.
If something goes wrong like a privacy complaint, a regulatory question, a client asking how their data was handled, this register is your evidence that you took reasonable steps.
As it says in the guide tab: "We didn't know" is not a defence. This document is.
This template won't replace professional advice. But it's the starting point every business needs and it's more than most businesses currently have.
Download the Free AI Approval Register — no sign-up required
At Hyplon, we advise and guide business owners and leaders on the governance and privacy strategy behind their AI, the obligations, the risks, and what to get right before and after they deploy. If you'd like an honest look at where your business stands, book a free 20-minute conversation — no pitch, no obligation.